As enterprises adopt AI agents, much of the identity conversation has understandably focused on identifying them, assigning owners, and managing their credentials. These are essential foundations. The next architectural question is how to preserve the meaning of that identity and authority throughout a changing sequence of actions.
An agent may begin with a legitimate task, discover additional tools, delegate part of the work, and encounter information that changes its next step. The enterprise needs a way to establish whether each consequential action remains within the authority originally granted.
This is why I welcome NIST’s recent work on agentic identity. Its first blog, Back to the Future: Why Agentic AI Needs a Strong Identity Foundation, reinforces established IAM practices and warns about the risks of credential sharing, excessive access, and approval fatigue. The follow-up, Design Tenets for Agent Identity Management Systems, provides an initial set of ten principles. [1][2]
I read this work as an invitation to connect identity management more closely to execution. That has practical implications for credentialing, runtime authorization, guardrails, and provenance and for how enterprises build on the IAM investments they already have.
A useful continuation of NIST’s earlier work
NIST has helped the industry develop a common language for these foundations over many years.
The SP 800-63 Digital Identity Guidelines establish guidance for identity proofing, authentication, and federation. Their focus is human digital identity; they should not be interpreted as a ready-made agent credentialing standard. They show why identity assurance should stay separate from other security decisions. [3]
SP 800-162, NIST’s guidance on attribute-based access control, describes authorization using attributes of subjects, resources, operations, and environmental conditions. It provides a foundation for evaluating access in context. [4]
SP 800-207, Zero Trust Architecture, puts the protection of resources at the center and treats authentication and authorization as distinct functions. SP 800-207A develops this further for cloud-native applications, including service identities, gateways, and proxies that enforce granular policies across environments. [5][6]
More recently, IR 8587 addresses the protection of identity tokens, access tokens, and assertions against forgery, theft, and misuse. Credential and token security remains essential as agents become consumers of enterprise services. [7]
The agentic work builds on this broader body of practice. The NCCoE’s February 2026 draft concept paper, Accelerating the Adoption of Software and AI Agent Identity and Authorization, asks practical questions about agent identification, dynamic permissions, delegation, intent, and verifiable audit records. [8]
Its subsequent comment summary reports more than 600 responses, with strong support for evolving existing standards. The project anticipates implementation resources and an eventual SP 1800-series practice guide. These tenets are an initial design framework, with standards and implementations still developing. [9][10]
That combination of industry engagement and implementation work is valuable. Enterprises need architectures that can operate across the systems they actually use.
Reading the tenets as a connected architecture
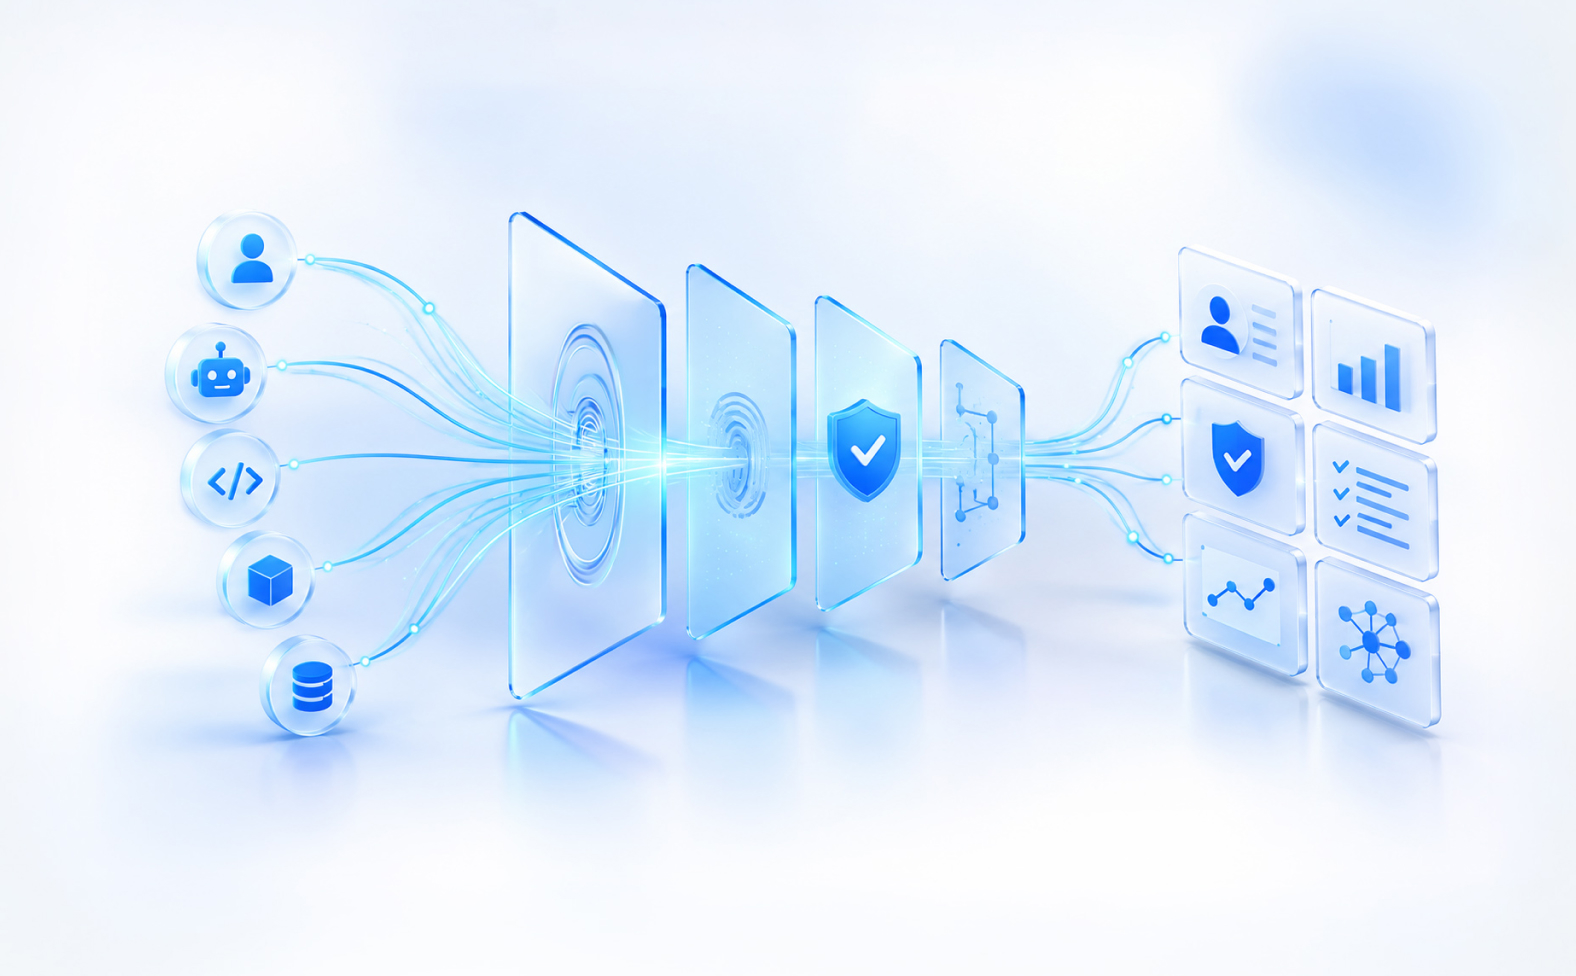
I find it useful to organize the tenets into five connected responsibilities. The grouping below is my interpretation; the numbered topics paraphrase NIST’s tenets. [2]

The implementation discussion that follows is my perspective on how these responsibilities should work together.
Credentialing must distinguish the agent, its sponsor, and its task
From a credentialing standpoint, I would separate three questions: which workload is this, on whose authority is it acting, and what has it been authorized to accomplish?
An agent identity can establish a durable relationship with an enterprise owner, approved software, and an operating environment. An individual execution also needs a distinguishable context: the task, participating agent instance, initiating principal, and relevant delegation.
These need not all be represented by permanent directory objects. They do need reliable identifiers and verifiable associations.
It also helps to distinguish an identity credential from an access grant. A workload certificate may authenticate an agent. An access token may convey scoped authorization to a service. A mandate may express an approved objective and constraints. Their formats and functions can differ; the architecture must connect them.
Consider a coding agent tasked with fixing a defect in one repository. Its sponsor may have access to many repositories and production infrastructure. The agent’s task needs a narrower boundary: inspect the relevant code, make changes in an approved workspace, run tests, and submit a pull request.
The task does not require the sponsor’s full authority. Issuing the agent a distinct credential is a start; issuing and enforcing appropriately bounded authority makes that distinction useful.
Delegation needs enforceable attenuation
Suppose the coding agent asks a second agent to analyze test failures. That second agent may need selected source files and test results. It does not automatically need permission to merge changes, modify deployment settings, or delegate unrestricted access onward.
This is the practical meaning of attenuation: authority becomes narrower as work is delegated.
OAuth Token Exchange offers mechanisms for representing delegation, including distinctions between the subject and an acting party. However, token exchange alone does not establish the enterprise’s task boundary. The issuer and receiving service must apply policy to the resulting authority. [11]
For implementation, I would test attenuation across operations, resources, audience, duration, and further delegation. A downstream service with broad technical privileges must still honor the narrower authority of the request it is fulfilling.
For an on-behalf-of workflow, effective authority should respect the intersection of the delegator’s permitted authority, the agent’s own boundary, the task’s constraints, and the receiving service’s policy. Separately authorized workflows may operate under organizational authority; that authority must be explicit.
A recorded parent-child relationship is useful provenance. Enforced limits at each delegation make it a security control.
Runtime authorization connects credentials to consequences
Even a well-scoped token may leave important decisions to the resource or tool receiving it. Permission to invoke a repository tool, for example, may cover several operations with very different consequences.
A runtime check should therefore evaluate the concrete action and relevant parameters. Reading a file, deleting a branch, exporting repository contents, and changing a workflow definition should be distinguishable operations.
The policy decision should incorporate verified identity, delegated authority, resource sensitivity, task constraints, and current conditions. Cedar illustrates a useful decision model: evaluate the principal, action, resource, and context against policy. [12]
The enforcement point then needs to bind that decision to the operation actually executed. A check against one destination or repository must not authorize a later request with different parameters.
Short-lived credentials help limit exposure, but revocation and containment also depend on enforcement behavior. Enterprises should understand cache lifetimes, queued jobs, downstream credentials, and operations already in progress.
This is where IAM becomes operational at action boundaries. Governed authority must remain meaningful when the agent reaches a tool, API, data service, or privileged operation.
For a business leader, the translation is simple. Agents stay in pilots until security can show that every consequential action was checked against the authority behind it. Connecting identity to execution is what lets them move into production.
Intent and behavior add context to the permission boundary
A task boundary expresses more than a list of accessible systems. It describes why access was granted and the constraints under which it may be used.
For the coding agent, reading a related test file may support the approved fix. Searching unrelated repositories for secrets is a different trajectory, even if both activities are technically possible through available tools.
I see intent and behavior-based access control (IBAC) as a practical extension of contextual authorization:
- Intent supplies the approved objective and constraints.
- Behavior supplies evidence from the evolving sequence of actions.
- Policy determines what that evidence means for the next operation.
The approved objective must come from an authorized originator or governed workflow. An agent’s explanation of its own actions is an input to assess, not a source of authority.
Some checks are explicit: repository scope, prohibited commands, allowed destinations, or whether production writes are permitted. Others require interpretation: whether repeated tool calls, unusual data collection, or a new delegation pattern remain consistent with the task.
Behavioral analysis can identify reasons to reduce access, pause execution, or request review. A favorable assessment must never override a hard prohibition.
This also places a limit on the term “deterministic.” A policy engine can apply a rule predictably to supplied inputs while an intent-alignment or anomaly signal remains probabilistic. Reliable enforcement requires attention to both the rule and the quality, freshness, and origin of its inputs.
My view is that approved purpose should shape the permission boundary, while observed behavior helps determine whether continued execution remains appropriate.
Guardrails need authority outside the reasoning loop
An instruction such as “never modify production” is useful guidance. An independently enforced policy that denies production writes establishes a stronger boundary.
A practical architecture layers several controls. Content and model guardrails screen suspicious input and output, sandboxing restricts the execution environment, runtime authorization governs tool use and resource operations, and credential controls limit what authority exists to be exercised.
These controls should reinforce one another. For a coding agent, a sandbox may limit the workspace, while repository and API policies govern what it can retrieve, change, or publish beyond that workspace.
The enterprise should also predefine responses. An explicit policy violation can be denied immediately. A behavioral anomaly may justify a narrower response, such as removing write access or pausing a task pending review.
Human approval belongs at consequential exceptions. It should cover a specific action, resource, and set of conditions, with execution held until that approval is validated. Where the stakes are high, it should go to an accountable approver other than the person who started the task. A developer approving their own agent’s fortieth request of the day is not exercising oversight; NIST’s tenets call this consent fatigue. A broader task or changed parameters may require a fresh decision.
The goal is to make oversight effective at agent speed while keeping responsibility with the enterprise.
Provenance belongs in the decision path
Before an action, the system needs to establish where the claimed authority and relevant inputs came from. A signed delegation from an authorized issuer has different significance from an unverified statement in a prompt. Data returned by an external tool should not acquire the authority of the task originator merely because the agent reads it.
After execution, the enterprise needs evidence linking the principal, agent instance, task, delegation, policy decision, and actual outcome.
For consequential operations, I would preserve the mandate reference, relevant authority limits, requested parameters, policy version, risk signals, approvals, and enforcement result. This supports investigation, policy improvement, and explanation of both permitted and blocked actions.
A signature can establish origin and integrity under a trusted key; it does not establish that an action was appropriate. Similarly, logging a decision does not prove that the downstream operation matched it. Evidence must connect authorization to execution.
Protected, append-only records require an independent collection and storage design. Sensitive prompts and payloads need not be copied indiscriminately: controlled references, hashes, access restrictions, and retention policies can preserve the evidence investigators need while limiting exposure.
Extend the IAM architecture around execution
These responsibilities can build on existing enterprise investments.

Actual products span these responsibilities. The practical step is to map the controls already deployed and identify where authority or evidence is lost between systems.
The gap to address is often the connection between an approved entitlement and a changing agent execution. Solving it may require policy orchestration, better enforcement coverage, delegation-aware decisions, and a shared evidence model.
That is also why authorization deserves treatment as enterprise infrastructure. Agents will cross platforms and invoke services whose owners should not each have to invent a separate interpretation of task authority.
Build confidence across the entire execution
What I value in NIST’s contribution is the way it gives practitioners a common basis for this work. Identity assurance, contextual authorization, workload security, and accountability all have substantial foundations. Agentic systems require us to connect them more deliberately.
I would start with one meaningful workflow and follow its authority end to end: from the initiating principal to the agent, through each delegation, into every consequential operation, and back through the evidence.
That exercise reveals whether credentials are appropriately scoped, policy is enforceable, behavioral changes influence access, and actions can be reconstructed.
The opportunity is to make established IAM investments work coherently throughout autonomous execution. That is how enterprises can give agents useful freedom while retaining control over the authority they exercise.
Reva AI is focused on runtime authorization for AI agents. To see these ideas applied to coding agents, start a free trial [https://agentsecurity.reva.ai/register].
References
- NIST, Design Tenets for Agent Identity Management Systems, October 27, 2026.
- NIST NCCoE, Accelerating the Adoption of Software and AI Agent Identity and Authorization, draft concept paper, February 2026.
- NIST NCCoE, Summary of Comments on the Concept Paper.
- NIST NCCoE, Project Resource Hub.
- Cedar, How Cedar Authorization Works.
The architectural groupings, examples, and recommendations are the author’s interpretation. IBAC is used here as an architectural approach, not as a NIST-defined standard or requirement.